2026-10-09
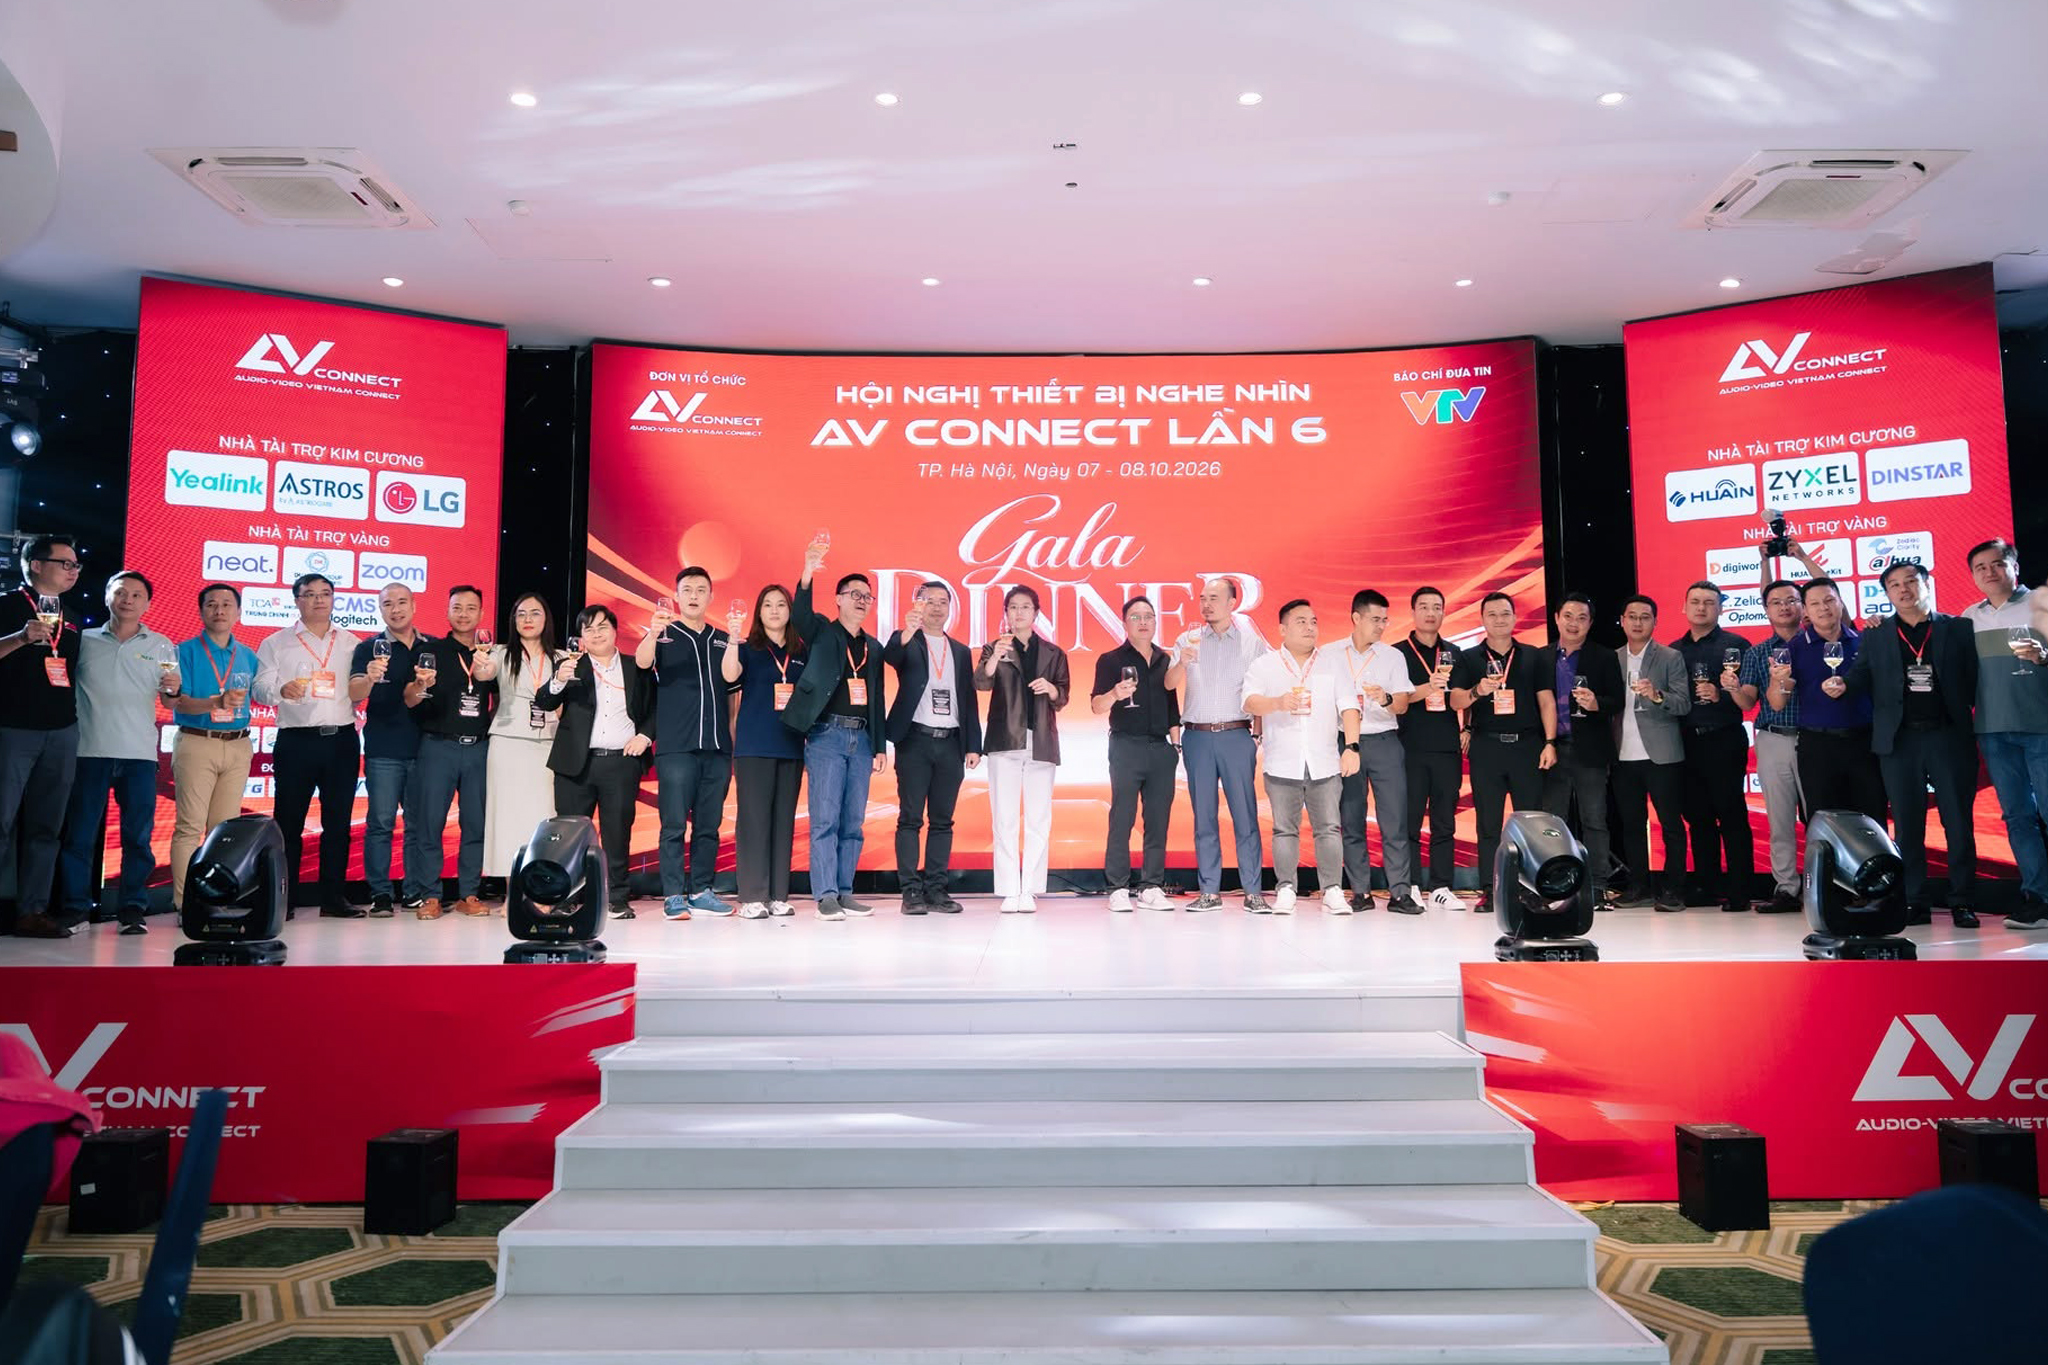
DINSTAR Participates in AV CONNECT Hanoi 2026 as Diamond Sponsor
PHP is a third-party, open-source programming language widely used to develop websites and web applications. On October 21, 2026, the PHP project released emergency patches for two critical remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619 (CVSS v4.0: 9.2), collectively known as “PHP2Shell.”
Following a comprehensive assessment of our product portfolio and cloud services, DINSTAR has determined that its products and services are not affected by CVE-2026-109618 and CVE-2026-109619.
We remain committed to product security and will provide updates if new information becomes available.
For questions, please contact us at support@dinstar.com.